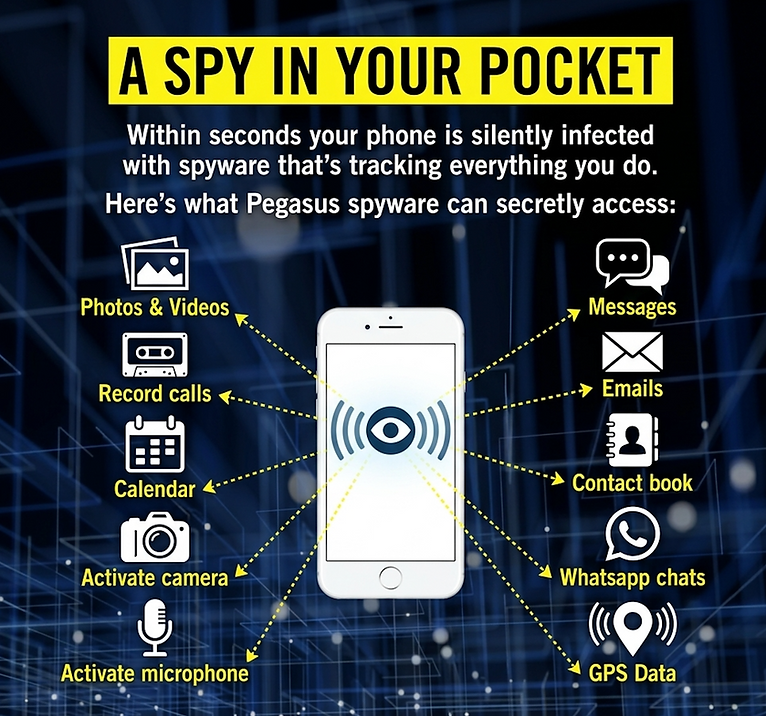
How an Operation Works
Reconstructed from Amnesty's 16 July 2026 reading of NSO documents filed in the WhatsApp case. Product-doc claims are labeled as company materials, not independent audits.
From Amnesty Security Lab's 16 July 2026 analysis of NSO documents in the WhatsApp case, a Pegasus operation runs as follows:
The customer-side dashboard accepts a target phone number.
The system fingerprints the device — OS, apps, network — including HLR lookups.
The operator picks a vector: Covert (zero-click), Triggered (one-click), network injection, or physical access.
Infection is delivered through NSO-managed anonymized infrastructure — the Pegasus Anonymizing Transmission Network.
Customer-specific accounts and domains ('White Services') are created so delivery looks like ordinary traffic.
Roles include analyst, operator, supervisor, and administrator on the customer-side console.
Exfiltrated data lands on customer-controlled storage servers, not NSO's.
An NSO network-operations function watches alerts on the delivery infrastructure.
Clustering infections to one customer
Customer-specific iCloud or Gmail accounts used in Apple vectors have let researchers cluster infections to one customer. Amnesty's July 2026 analysis says internal NSO systems (Sales 3, Sales 6 demo systems, employee test numbers) line up with clusters in the Pegasus Project leak.
Licensing controls — company materials, not audits
Product docs describe licensing controls including target caps and barred countries. NSO has said US numbers and Israeli numbers are excluded. These are company controls described in product documents, not proof of compliance.